
Entende o contexto
Lê a operação, o cliente e o histórico antes de propor qualquer coisa.
Vendas, marketing, atendimento, operação, financeiro e inteligência trabalhando sobre o mesmo contexto — para sua empresa ganhar escala sem perder controle.
Sua empresa inteira. Uma operação. IA trabalhando.
Para empresas de qualquer setor que querem crescer com estrutura, controle e inteligência.
Painel ilustrativo do Sistema Centriu com sete frentes trabalhando: atendimento, comercial, operação, agentes, inteligência, conteúdo e marketing. Cada frente mostra o trabalho concluído ou o próximo passo.
Representação ilustrativa do trabalho em execução
Não é falta de ferramenta. É que cada ferramenta resolve um pedaço, e ninguém é dono do todo. O custo disso não aparece numa fatura — aparece no mês seguinte.
Sistemas que não se falam
O mesmo dado é digitado de novo — e cada cópia conta uma história diferente.
Dados duplicados
Ninguém sabe qual versão é a verdadeira na hora de decidir.
Conversas perdidas
O cliente repete o contexto a cada canal e a cada pessoa.
Tarefas espalhadas
O trabalho vive em planilhas, mensagens e na memória de alguém.
Decisões sem contexto
A escolha é feita com o recorte que estava à mão, não com o que importava.
Automações desconectadas
Cada ferramenta automatiza um pedaço e ninguém enxerga o todo.
Nenhum desses problemas se resolve comprando mais um software. Eles se resolvem quando a operação inteira passa a trabalhar sobre o mesmo contexto.
A Centriu não é uma coleção de produtos. É uma plataforma em que clientes, áreas e agentes leem e escrevem no mesmo lugar.
Cliente 360
Um contexto, não vários cadastros
Cada conversa, tarefa, campanha, cobrança e decisão fica ligada ao cliente e à operação — não a um sistema isolado.
As áreas abaixo são partes da mesma operação, não produtos separados. Elas compartilham conta, permissões e histórico.
A inteligência artificial da Centriu participa da operação: entende contexto, prepara trabalho, executa rotinas e pede aprovação quando importa.
Lê a operação, o cliente e o histórico antes de propor qualquer coisa.
Redige, organiza, calcula e deixa pronto para revisão humana.
Roda o que é repetitivo dentro dos limites definidos pela empresa.
Cruza áreas, identifica prioridade e mostra o motivo da recomendação.
O que é sensível passa por uma pessoa antes de valer. Sem exceção silenciosa.
Registra o que aconteceu e usa o resultado para melhorar a próxima decisão.
Uma plataforma, várias frentes de trabalho. Tudo no mesmo contexto, com a IA participando do que dá para acelerar.
CRM, pipeline, oportunidades, propostas, follow-up e automações.
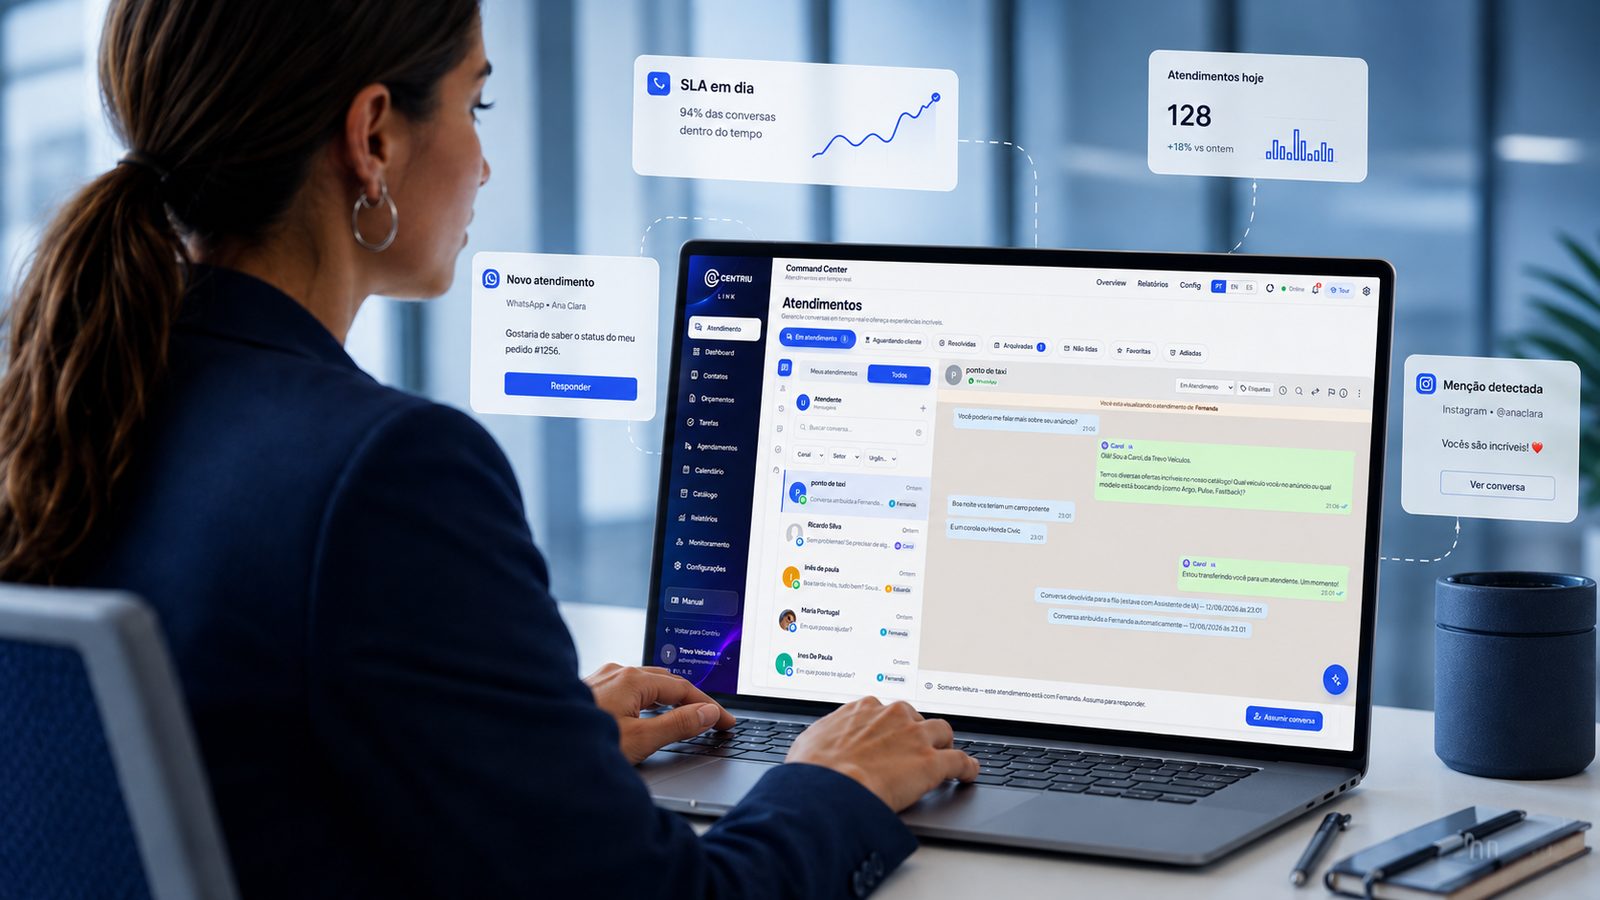
WhatsApp, Instagram, Messenger, chat do site e e-mail no mesmo contexto.
Tarefas, responsáveis, prazos, aprovações, agenda e capacidade.
Contas, cobranças, caixa, fiscal, margem, IR, orçamento e inteligência econômica.
Planejar, produzir, aprovar, publicar e medir conteúdo e campanhas.
Painéis, alertas, previsões, recomendações e leitura executiva.
Rotinas executadas continuamente pela IA com controle e aprovação.
Diagnóstico, estratégia, transformação, acompanhamento e especialistas.
A Centriu faz sentido quando o volume aumenta e a estrutura precisa acompanhar. Não é sobre setor nem tamanho: é sobre a operação conseguir sustentar o próximo estágio.
As vendas crescem, mas o processo não acompanha.
As áreas trabalham separadas e o cliente sente.
A operação depende de pessoas específicas.
O financeiro ficou complexo e o caixa perde visibilidade.
O atendimento cresce em volume e em canais.
A IA entra sem contexto, controle ou histórico.
Se a empresa ainda não começou a crescer, a Centriu também ajuda a preparar a estrutura para o primeiro salto.
Ver a Centriu funcionandoA Centriu combina tecnologia, inteligência, método e acompanhamento. A consultoria diagnostica, desenha, implanta e acompanha — com evidências, não com apresentação.
Diagnóstico e imersão na operação
Estratégia e prioridades
Roadmap de transformação
Desenho da arquitetura operacional
Implantação conduzida
Acompanhamento com evidências
Benchmarking e leitura de mercado
Especialistas, rede e inteligência coletiva
Uma conversa para entender onde a sua operação perde tempo, dinheiro ou capacidade — e o que a Centriu faria primeiro.
problema
Centriu Run's natural-language operations command feature is a chat box. It was meant to answer questions about operations using an AI backend. It failed on every single question asked to it. This happened since the day its edge function was renamed. The rename was from an earlier, related feature. The cause was that the frontend's request to that edge function was missing both authentication headers. The function requires these two headers. They were lost silently during that earlier rename. The edge function checks for authentication before running any of its own logic. So, every request was rejected with HTTP 401. This happened before the AI backend was ever reached. The interface always showed a general "Error: HTTP 401" and nothing else. The proof this was total, not partial, was clear. The history table the function writes to on every successfully answered question had exactly zero rows. This means no question had ever been answered through this interface. Unused imports for the exact functions needed to build those headers were still in the file. This is direct proof the header-sending code once existed. It was deleted by accident, not that it was never written. The fix restores both headers. It also keeps the server's own specific error detail. This is better than just a status code. So, a future failure can be understood, not just a mystery.
A feature that fails loudly and inconsistently gets noticed and reported quickly. Someone hits an error, describes it, and it gets triaged. A feature that fails the exact same way every single time, from the very first day it shipped, is a different and more dangerous kind of invisible. There's no "it used to work" moment to notice. There's no intermittent success to contrast the failure against. A person trying it once and seeing a general error message has no way to tell if the feature is broken. They also don't know if they simply asked a bad question. The failure blends into the background as "this feature apparently doesn't work well." It does not show up as the specific, fixable problem it actually is.
A feature that fails loudly and inconsistently gets noticed and reported quickly. Someone hits an error, describes it, and it gets triaged. A feature that fails the exact same way every single time, from the very first day it shipped, is a different and more dangerous kind of invisible. There's no "it used to work" moment to notice. There's no intermittent success to contrast the failure against. A person trying it once and seeing a general error message has no way to tell if the feature is broken. They also don't know if they simply asked a bad question. The failure blends into the background as "this feature apparently doesn't work well." It does not show up as the specific, fixable problem it actually is.
The problem was found during a wider check of Run's settings screens. Its main cause goes back to an earlier, unrelated change. The natural-language command feature's edge function had been renamed. It was renamed from an older, related function used for a different purpose. During that rename, two headers were dropped from the fetch call. The calling code needs to send these headers. They are an API key header and a bearer authorization token. The target edge function runs with strict JWT verification. This means it checks who is calling before it runs any of its own code. So, every request without valid login details was rejected right away with HTTP 401.
The proof this was a complete, 100% failure, not just sometimes, is clear and can be measured. The database table the edge function writes to for every question answered successfully had exactly zero rows. This was not a small number. It was not a recent gap. It was zero, for all the time the feature was available. To make the diagnosis harder, two unused import statements were still in the file. These were for the exact functions needed to make those missing headers. They were not used by any code. This clearly shows that the code for sending headers used to be in this file. It was deleted, most likely by accident during the rename. It was not that the feature was shipped incomplete from the start.
The fix puts both headers back into the request. The API key header is set to the project's public anonymous key. The bearer authorization header is set to the user's own saved access token if one exists. If not, it uses the anonymous key. This matches the same pattern used by a similar feature elsewhere in the product. The fix does more than just restore basic function. Before, the request just showed a simple HTTP status code with no details. Now, it tries to read and include the server's own error message. This message is capped at 200 characters. This is so a future failure, no matter the cause, shows a message that can be understood. It will not be a status code that looks the same whether the problem is an AI usage limit, a bad question, or something else.
Both needed authentication headers (API key and bearer authorization token) are restored. They are on every request to the natural-language command edge function.
The user's own saved access token is used when available. If not, it uses the anonymous key. This is the same authentication pattern already used by a similar feature elsewhere in the product.
Error messages now keep the server's own specific detail (up to 200 characters). This is instead of reporting a simple, undifferentiated status code.
A problem was measured with clear proof before the fix. A special history table had exactly zero rows. This proved a total, not partial, failure. It was not treated as a suspected or theoretical issue.
The main cause was traced to a specific prior change. This was a rename from a different, related edge function. It was confirmed by unused imports left in the file. It was not just guessed at.
No change to the AI backend or its own logic. The fix is only about the authentication headers on the calling request. The backend itself was never reached before the fix.
A feature that had answered zero questions since it shipped now truly answers them. Every request now reaches the backend it was always meant to reach. The fix also keeps the server's own error detail instead of just a status code. So, a future failure (a usage limit, a bad request, anything else) now shows up as something a person can act on. It is not the same unclear message this feature always produced before.
A feature that had answered zero questions since it shipped now truly answers them. Every request now reaches the backend it was always meant to reach. The fix also keeps the server's own error detail instead of just a status code. So, a future failure (a usage limit, a bad request, anything else) now shows up as something a person can act on. It is not the same unclear message this feature always produced before.
Someone opens the operations command box. They ask a simple question about the current workload. Before the fix, this always showed the same general "Error: HTTP 401." This happened no matter the question. The request never got past the edge function's own authentication check. After the fix, the same question reaches the AI backend. It gets a real answer. It is logged as a real row in the history table for the first time.
The database table the edge function writes to on every successfully answered question had exactly zero rows. This was for all the time the feature was available. This was direct, measurable proof, not just a guess.
Two needed authentication headers were dropped from the request. This happened during an earlier, unrelated rename of the edge function. The function's own strict authentication check then rejected every request. This happened before its logic ever ran.
The exact import statements needed to build those headers were still in the file. They were not used by any remaining code. This is a clear sign of code that used to exist and was deleted.
No. The fix is only about putting the authentication headers back on the request. The AI backend and its logic were never the real problem. They were never being reached at all.
The error now includes the server's own specific detail (up to 200 characters). This is instead of a simple status code. So, a future failure can be understood, not just a mystery.
It is sold by subscription with a published starting price. The exact current values are on the central pricing page.
Centriu Run's natural-language operations command feature is a chat box. It was meant to answer questions about operations using an AI backend. It failed on every single question asked to it. This happened since the day its edge function was renamed. The rename was from an earlier, related feature. The cause was that the frontend's request to that edge function was missing both authentication headers. The function requires these two headers. They were lost silently during that earlier rename. The edge function checks for authentication before running any of its own logic. So, every request was rejected with HTTP 401. This happened before the AI backend was ever reached. The interface always showed a general "Error: HTTP 401" and nothing else. The proof this was total, not partial, was clear. The history table the function writes to on every successfully answered question had exactly zero rows. This means no question had ever been answered through this interface. Unused imports for the exact functions needed to build those headers were still in the file. This is direct proof the header-sending code once existed. It was deleted by accident, not that it was never written. The fix restores both headers. It also keeps the server's own specific error detail. This is better than just a status code. So, a future failure can be understood, not just a mystery.