
Entende o contexto
Lê a operação, o cliente e o histórico antes de propor qualquer coisa.
Vendas, marketing, atendimento, operação, financeiro e inteligência trabalhando sobre o mesmo contexto — para sua empresa ganhar escala sem perder controle.
Sua empresa inteira. Uma operação. IA trabalhando.
Para empresas de qualquer setor que querem crescer com estrutura, controle e inteligência.
Painel ilustrativo do Sistema Centriu com sete frentes trabalhando: atendimento, comercial, operação, agentes, inteligência, conteúdo e marketing. Cada frente mostra o trabalho concluído ou o próximo passo.
Representação ilustrativa do trabalho em execução
Não é falta de ferramenta. É que cada ferramenta resolve um pedaço, e ninguém é dono do todo. O custo disso não aparece numa fatura — aparece no mês seguinte.
Sistemas que não se falam
O mesmo dado é digitado de novo — e cada cópia conta uma história diferente.
Dados duplicados
Ninguém sabe qual versão é a verdadeira na hora de decidir.
Conversas perdidas
O cliente repete o contexto a cada canal e a cada pessoa.
Tarefas espalhadas
O trabalho vive em planilhas, mensagens e na memória de alguém.
Decisões sem contexto
A escolha é feita com o recorte que estava à mão, não com o que importava.
Automações desconectadas
Cada ferramenta automatiza um pedaço e ninguém enxerga o todo.
Nenhum desses problemas se resolve comprando mais um software. Eles se resolvem quando a operação inteira passa a trabalhar sobre o mesmo contexto.
A Centriu não é uma coleção de produtos. É uma plataforma em que clientes, áreas e agentes leem e escrevem no mesmo lugar.
Cliente 360
Um contexto, não vários cadastros
Cada conversa, tarefa, campanha, cobrança e decisão fica ligada ao cliente e à operação — não a um sistema isolado.
As áreas abaixo são partes da mesma operação, não produtos separados. Elas compartilham conta, permissões e histórico.
A inteligência artificial da Centriu participa da operação: entende contexto, prepara trabalho, executa rotinas e pede aprovação quando importa.
Lê a operação, o cliente e o histórico antes de propor qualquer coisa.
Redige, organiza, calcula e deixa pronto para revisão humana.
Roda o que é repetitivo dentro dos limites definidos pela empresa.
Cruza áreas, identifica prioridade e mostra o motivo da recomendação.
O que é sensível passa por uma pessoa antes de valer. Sem exceção silenciosa.
Registra o que aconteceu e usa o resultado para melhorar a próxima decisão.
Uma plataforma, várias frentes de trabalho. Tudo no mesmo contexto, com a IA participando do que dá para acelerar.
CRM, pipeline, oportunidades, propostas, follow-up e automações.
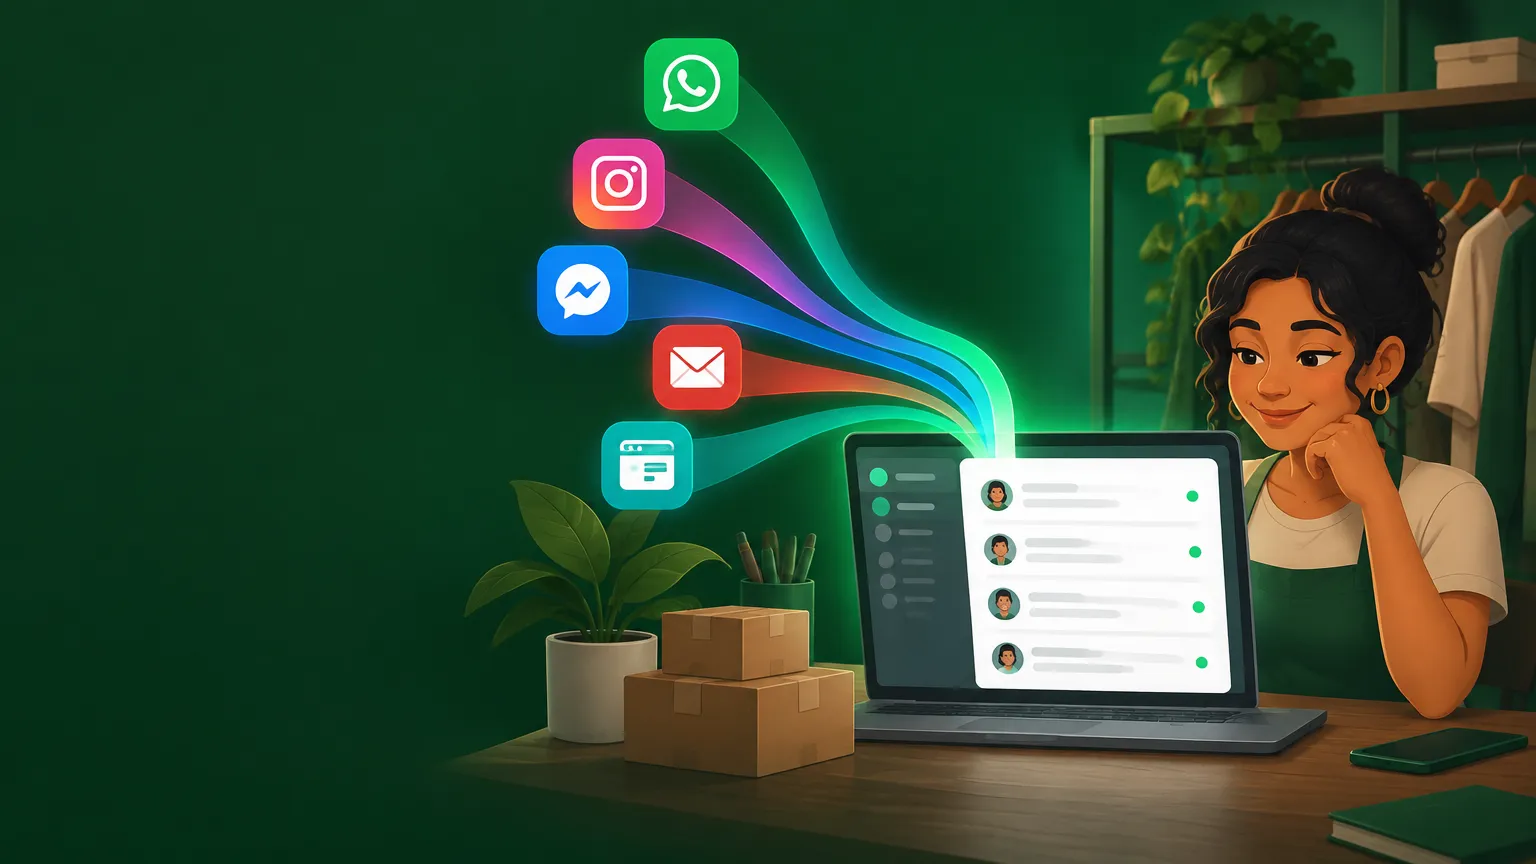
WhatsApp, Instagram, Messenger, chat do site e e-mail no mesmo contexto.
Tarefas, responsáveis, prazos, aprovações, agenda e capacidade.
Contas, cobranças, caixa, fiscal, margem, IR, orçamento e inteligência econômica.
Planejar, produzir, aprovar, publicar e medir conteúdo e campanhas.
Painéis, alertas, previsões, recomendações e leitura executiva.
Rotinas executadas continuamente pela IA com controle e aprovação.
Diagnóstico, estratégia, transformação, acompanhamento e especialistas.
A Centriu faz sentido quando o volume aumenta e a estrutura precisa acompanhar. Não é sobre setor nem tamanho: é sobre a operação conseguir sustentar o próximo estágio.
As vendas crescem, mas o processo não acompanha.
As áreas trabalham separadas e o cliente sente.
A operação depende de pessoas específicas.
O financeiro ficou complexo e o caixa perde visibilidade.
O atendimento cresce em volume e em canais.
A IA entra sem contexto, controle ou histórico.
Se a empresa ainda não começou a crescer, a Centriu também ajuda a preparar a estrutura para o primeiro salto.
Ver a Centriu funcionandoA Centriu combina tecnologia, inteligência, método e acompanhamento. A consultoria diagnostica, desenha, implanta e acompanha — com evidências, não com apresentação.
Diagnóstico e imersão na operação
Estratégia e prioridades
Roadmap de transformação
Desenho da arquitetura operacional
Implantação conduzida
Acompanhamento com evidências
Benchmarking e leitura de mercado
Especialistas, rede e inteligência coletiva
Uma conversa para entender onde a sua operação perde tempo, dinheiro ou capacidade — e o que a Centriu faria primeiro.
problema
When another Centriu screen hands context to Axiom — which record is open, what period is selected, what filters are active — that handoff follows a fixed protocol (`centriu.context/1`). This protocol treats the context as a ticket. It describes WHERE someone is. It never grants WHAT they can do. Fields that decide authority are refused on principle. These include organization, user, permissions, roles, and tenant. This happens even if a screen tries to send them. Values that look like a credential are caught by pattern. Examples are a JWT, a Supabase key, an OpenAI-style key, a GitHub or Slack token, a Google API key, a private-key block, or a Bearer header. This happens even under an innocent field name. Any key that would carry full document content is blocked outright. It is not trimmed. Every single field that gets removed is recorded. It has one of six named reasons. There is no silent discard. The resulting prompt block tells the model in plain language that the context grants nothing. It says that any real access still has to go through the owning tool. It also says that a refusal should be reported honestly. It should not be answered from memory.
Handing an assistant a bit of context about the screen someone is already on is a small, obviously useful thing. It means not having to re-explain which invoice or which deal is in focus. But that same channel, if left unguarded, is also the easiest place for a bug or a compromised client to slip in something that decides authority. This could be an organization ID, a role, or a permission flag. It hopes the assistant on the other end treats a screen's own claim as good enough. An internal AI that reaches across a whole company's modules needs a rule that never lets that shortcut work. It does not need a policy someone has to remember to enforce screen by screen.
Handing an assistant a bit of context about the screen someone is already on is a small, obviously useful thing. It means not having to re-explain which invoice or which deal is in focus. But that same channel, if left unguarded, is also the easiest place for a bug or a compromised client to slip in something that decides authority. This could be an organization ID, a role, or a permission flag. It hopes the assistant on the other end treats a screen's own claim as good enough. An internal AI that reaches across a whole company's modules needs a rule that never lets that shortcut work. It does not need a policy someone has to remember to enforce screen by screen.
Every context object that reaches Axiom carries a protocol version (`centriu.context/1`). It is read through one function, `sanitizarContexto()`. This function is shared byte-for-byte between the module's own app and every Edge Function that accepts context. A generation script keeps the two copies from silently drifting apart. It has a `--check` mode specifically built to catch that drift. Three fields are refused on principle even if a screen tries to send them. These are organization, user, and permissions. This also includes their common aliases like tenant, role, scopes, and entitlements. This is because authority in Axiom always comes from the caller's own verified identity. It never comes from a claim inside the context payload itself.
What IS allowed is narrow and shaped. This includes which system is handing off (a lowercase slug). It also includes which surface it came from (the Axiom screen itself, ChatGPT, or a system-to-system call). An optional area and route within that system are allowed. An entity being looked at is allowed. This includes a type and an opaque ID Axiom never interprets. It just passes it back to the tool that owns it. A selected date range in ISO format is allowed. A currency CODE only is allowed. Never a monetary value. A short list of filters is allowed. A list of capability hints a screen can offer as a navigation cue is allowed. These are re-verified against the real registry and the caller's own identity before anything is trusted. Every one of those fields has a hard character or item cap. This is because a context object is meant to be a ticket, not an attachment.
On top of the field allowlist, values themselves are checked. They are checked for the SHAPE of a credential. This happens regardless of which field they arrived in. Seven distinct patterns cover JSON Web Tokens. They cover both old- and new-format Supabase keys. They also cover OpenAI-style secret keys, GitHub personal-access tokens, Slack tokens, Google API keys, PEM-formatted private keys, and Bearer/Basic authorization headers. A key whose NAME suggests it carries full content is refused outright. This includes body, payload, an attached document, a transcript, a complaint, a medical or financial extract. It is not merely trimmed. This is because summarizing a document is a different operation from receiving one wholesale. Nested objects inside filters or metadata are stripped. This is for the same reason stated directly in the code's own comment. The context is shallow on purpose. This is because nesting is where a document hides.
None of this fails the whole request over one bad field. A single strange filter gets pruned. The removal is recorded under one of six named reasons. These are authority claim, looks like a secret, carries full content, text too long, wrong format, or over a numeric limit. That record travels all the way to Axiom's own audit trail. It goes alongside the call it accompanied. The model itself is then told, in a fixed block of plain language, exactly what the surviving context does and does not mean. It says WHERE someone is. It grants NOTHING. If a downstream tool refuses an action, the honest response is to report the refusal. It is not to try another path. It is not to state a remembered number as if it were current.
One shared sanitization function (`sanitizarContexto`) is built. It is generated identically into every Edge Function from a single source file. It has a `--check` script that catches the two copies drifting apart.
A fixed refusal list is built. This includes organization, user, permissions, tenant, role, scopes, and entitlements. These are removed on principle even if a sending screen includes them. They are never treated as a substitute for verified identity.
Seven credential-shape detectors are built. These include JWT, two Supabase key formats, OpenAI-style keys, GitHub tokens, Slack tokens, Google API keys, PEM private keys, and Bearer/Basic headers. They are checked against the VALUE. This is independent of which field name it arrived under.
Outright refusal is built. This is not truncation. It applies to any field whose name suggests it carries full document, transcript, or complaint content.
Hard numeric caps are built on every field. This includes system slug, area, route, entity type/ID/label, filter count, metadata count, and capability-hint count. This ensures a context object cannot grow into an attachment.
Six named removal reasons are built. Every single discard is logged. It is not dropped silently. This feeds the same audit trail the generic module tools already write to.
A screen can hand Axiom useful, specific context. This channel will never become a second, informal way to claim authority or leak a credential. Nothing that gets stripped disappears without a trace. Every removal is attributable to a specific, named reason. This matters the day someone asks why a particular filter didn't make it through. The sanitizer is generated from one source into every consumer. So, a fix made once cannot silently fail to reach an Edge Function. This would happen if it was written against an older copy of the rule.
A screen can hand Axiom useful, specific context. This channel will never become a second, informal way to claim authority or leak a credential. Nothing that gets stripped disappears without a trace. Every removal is attributable to a specific, named reason. This matters the day someone asks why a particular filter didn't make it through. The sanitizer is generated from one source into every consumer. So, a fix made once cannot silently fail to reach an Edge Function. This would happen if it was written against an older copy of the rule.
A screen hands Axiom context. This includes a filter whose value happens to match the shape of a Bearer authorization header. It was pasted in by mistake during testing. It was not a real attack. The sanitizer recognizes the VALUE's shape. It does not pass it through because the field name looked innocuous. It strips it. It records the removal under "looks like a secret." This is visible later in the audit trail. The rest of the context reaches the model exactly as sent. This includes which system, which entity, and which period.
No. Organization, user, permission, role and tenant fields are refused on principle from context payloads. Access is always decided by the caller's own verified identity. It is never decided by a claim inside the handoff.
It is caught by matching the shape of the VALUE against known credential patterns. These include JWT, Supabase, OpenAI-style, GitHub, Slack, Google, private keys, and Bearer/Basic headers. This happens regardless of which field name it arrived under. Then, it is removed.
No. Any field whose name suggests full content is refused outright. This includes body, payload, an attachment, a transcript, or a complaint. It is not shortened. Retrieving an actual document is a separate, authorized operation.
No. Every removal is recorded with one of six named reasons. It is logged to the audit trail that Axiom's generic module tools also write to.
The rule is generated from a single source file into every consumer. It has a script that specifically checks for drift between the copies.
It is sold by subscription with a published starting price. Exact current values are on the central pricing page.
When another Centriu screen hands context to Axiom — which record is open, what period is selected, what filters are active — that handoff follows a fixed protocol (`centriu.context/1`). This protocol treats the context as a ticket. It describes WHERE someone is. It never grants WHAT they can do. Fields that decide authority are refused on principle. These include organization, user, permissions, roles, and tenant. This happens even if a screen tries to send them. Values that look like a credential are caught by pattern. Examples are a JWT, a Supabase key, an OpenAI-style key, a GitHub or Slack token, a Google API key, a private-key block, or a Bearer header. This happens even under an innocent field name. Any key that would carry full document content is blocked outright. It is not trimmed. Every single field that gets removed is recorded. It has one of six named reasons. There is no silent discard. The resulting prompt block tells the model in plain language that the context grants nothing. It says that any real access still has to go through the owning tool. It also says that a refusal should be reported honestly. It should not be answered from memory.